Zillow Listing to RMM
Zillow Listing -> "Virtual Tour" -> Fake Zoom Url
Analysis
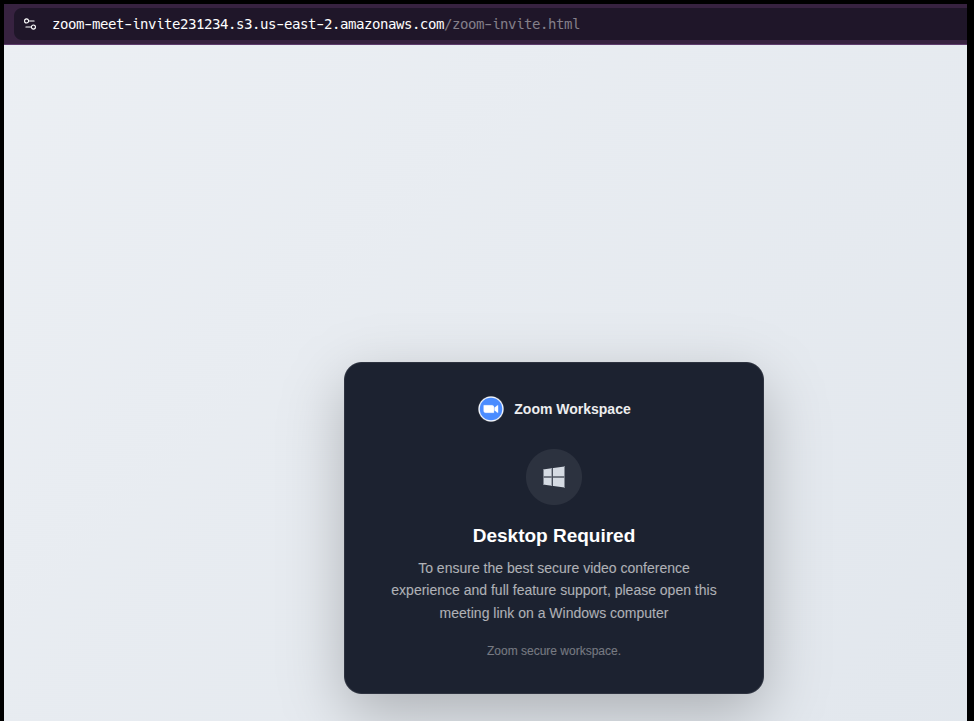
I browsed to that page on a linux device, and got the prompt about it requiring a Windows Desktop system to run. The fake zoom url:
zoom-meet-invite231234[.]s3[.]us-east-2[.]amazonaws[.]com/zoom-invite.html

I initially used browserling to access the link using a Microsoft Edge on a Windows device and I was able to access the fake zoom page. I then proceeded through all the prompts and was met with a download for a file called zoom.exe [db56557d0d20550a5b283196f8e4a41a10b931297463dbd3509b90b27408f035]
I switched back to my analysis linux workstation and changed by browser user agent using the browser dev tools and was also able to access the fake zoom landing page.
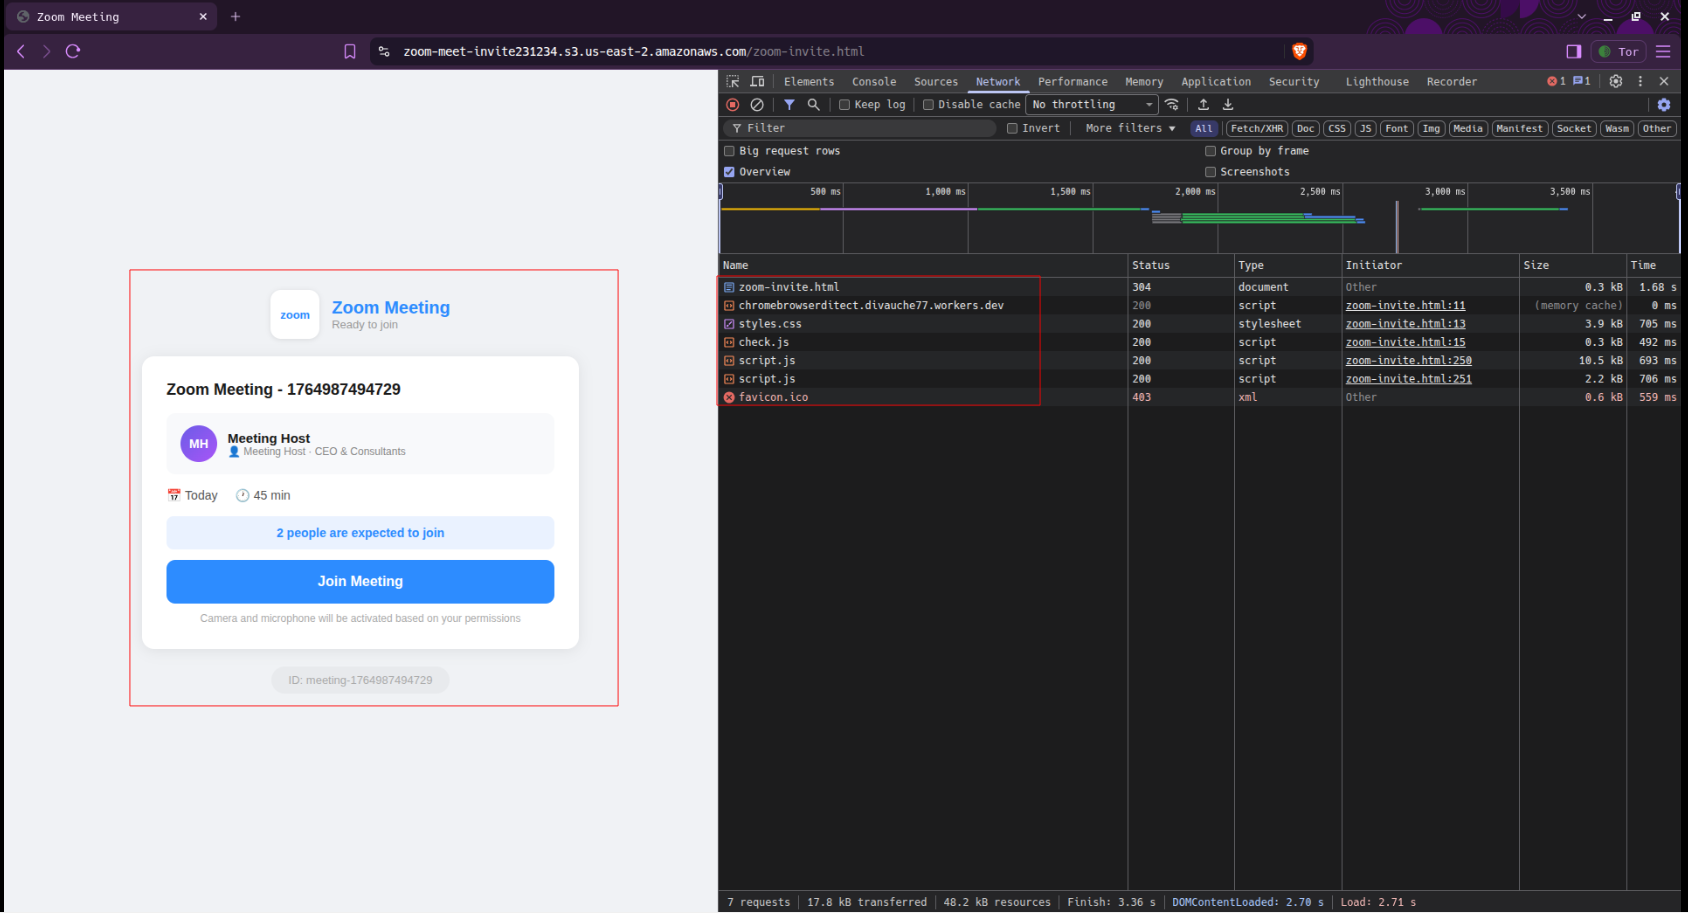

From the screenshot above, you can see some interesting javascript files being run in the background.
I saved those scripts on disk and had AI analyse them:
The landing page is a fully scripted, 6-screen fake Zoom "meeting" (zoom-invite.html):
- spinning "Connecting…" → fake loading → join card ("Meeting Host · CEO & Consultants", meeting-1764987494729, "2 people expected") → a fake active meeting with a running timer → "Update Required" with a 4s auto-countdown → a fake Microsoft Store page with "Update via Microsoft Store". script.js [the first one] (the flow driver) does the real work:
Blocks devtools: context menu, F12, Ctrl+Shift+I/J, Ctrl+U
Advances screens on timers so it feels live, fakes a download progress bar
downloadPayload(): injects a hidden and clicks the payload URL from PAYLOAD_CONFIG (silent download)
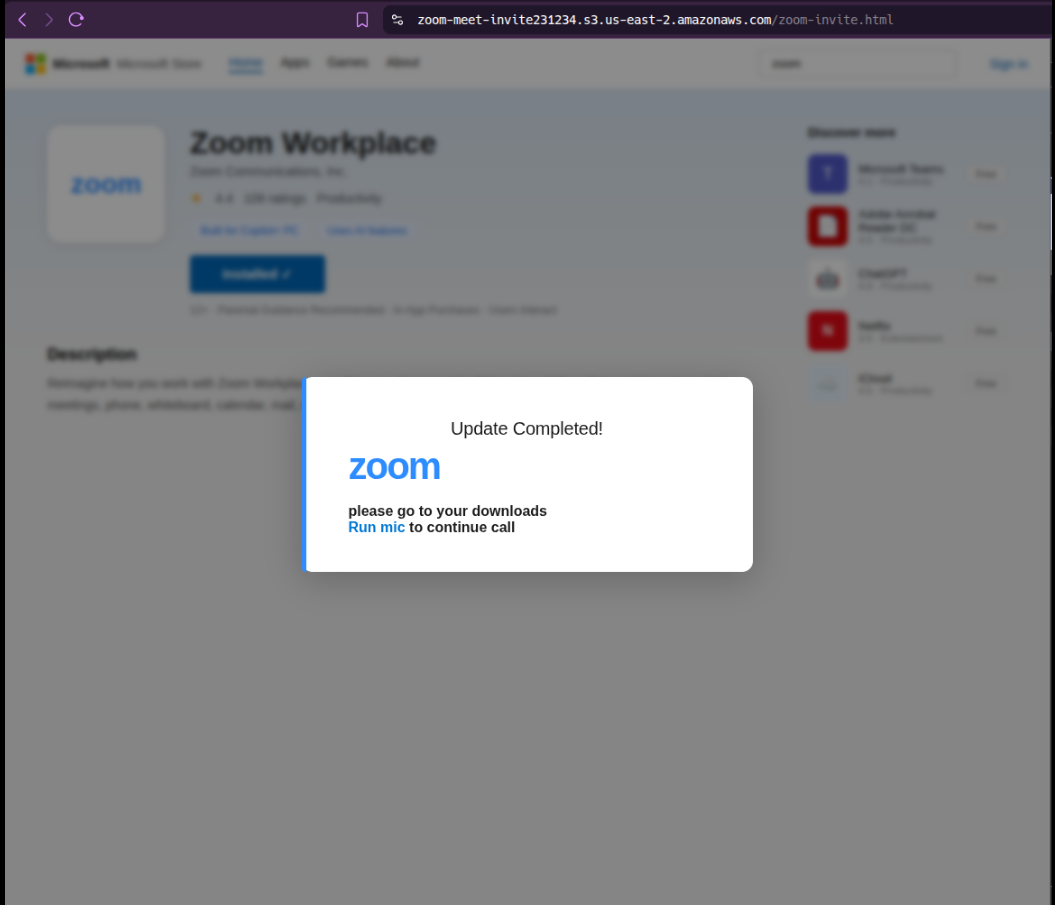
Shows a popup: "please go to your downloads and click Run mic to continue call" (the file is renamed .hta = executable shell)
reportDownload(): POSTs {file:'ZOOM CONNECT', downloadedAt, telegram:[...]} to downloadedreports[.]divauche77[.]workers[.]dev. script.js [the second one] is the quality gate: mobile → "Windows Desktop Required" panel, non-Windows → "Desktop Required". Only Windows-desktop victims reach the flow. check.js = one line, /* allowed */ — a pass-through "IP blocker". The biggest finds in the HTML's inline PAYLOAD_CONFIG:
Live payload: hxxps[://]pub-1e9d6c57f6d543e99a4570a07bbe26ad[.]r2[.]dev/zoom.exe (Cloudflare R2) — that's where your zoom.exe came from
A live Telegram bot token → chat_id 6955571616: the attacker gets pinged every time someone downloads (configurable exfil)
Ops switch payload wrappers per campaign: type:'hta'/run_mic.hta here, type:'vbs'/document.vbs on the Lambda fallback URL — same lure, different droppers. So the JS's job: make the victim believe they're joining a real Zoom meeting, panic them with a fake "critical update", then silently drop malware and notify the attacker via Telegram.
I proceeded to download zoom.exe for further analysis. I ran capa on the file and the most interesting rule that stood out to me was that the file contained an embedded file.
Sucessful download page:

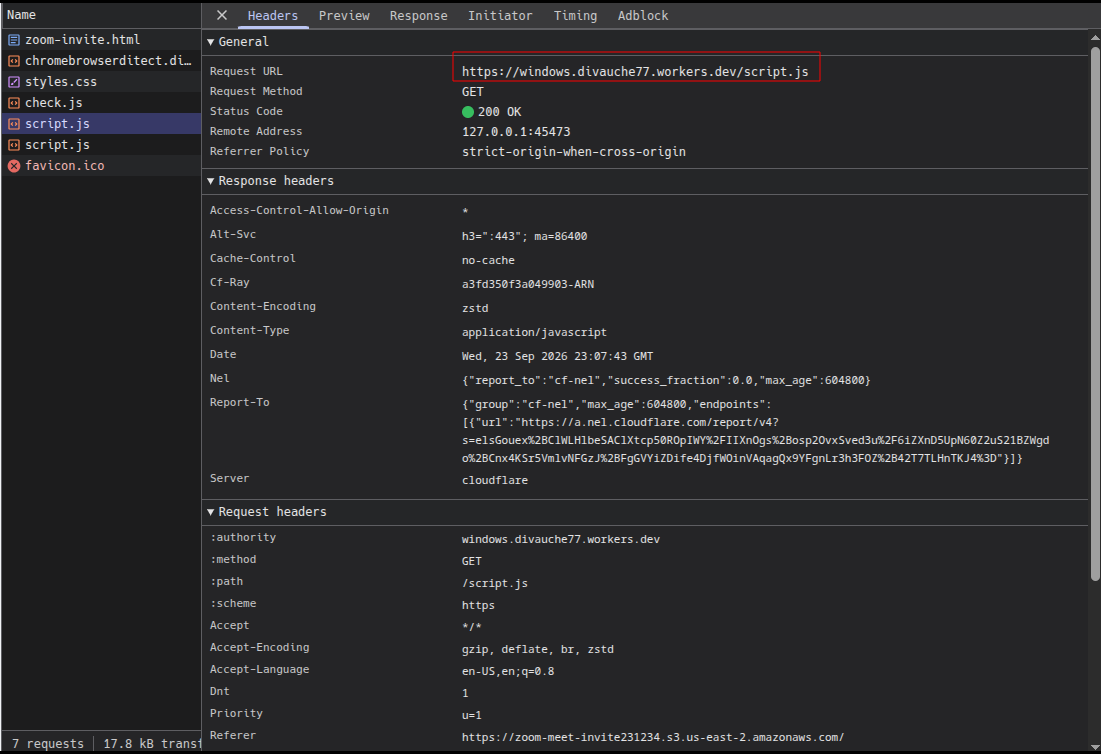
Some info from the .js files:

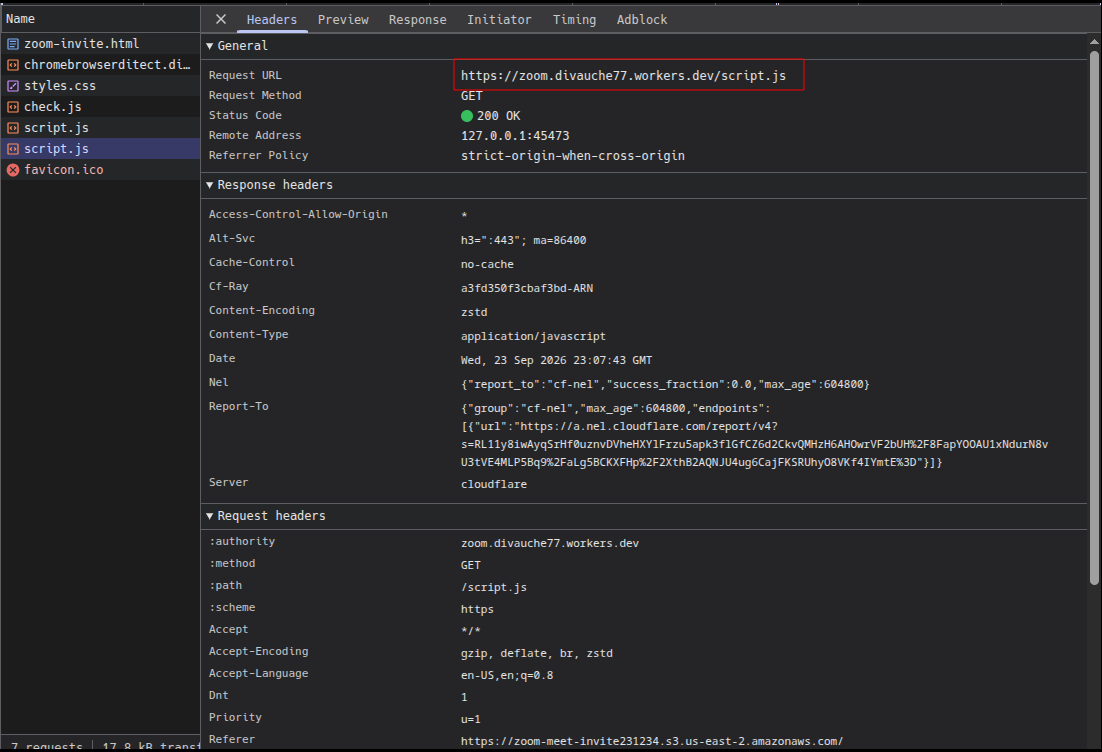

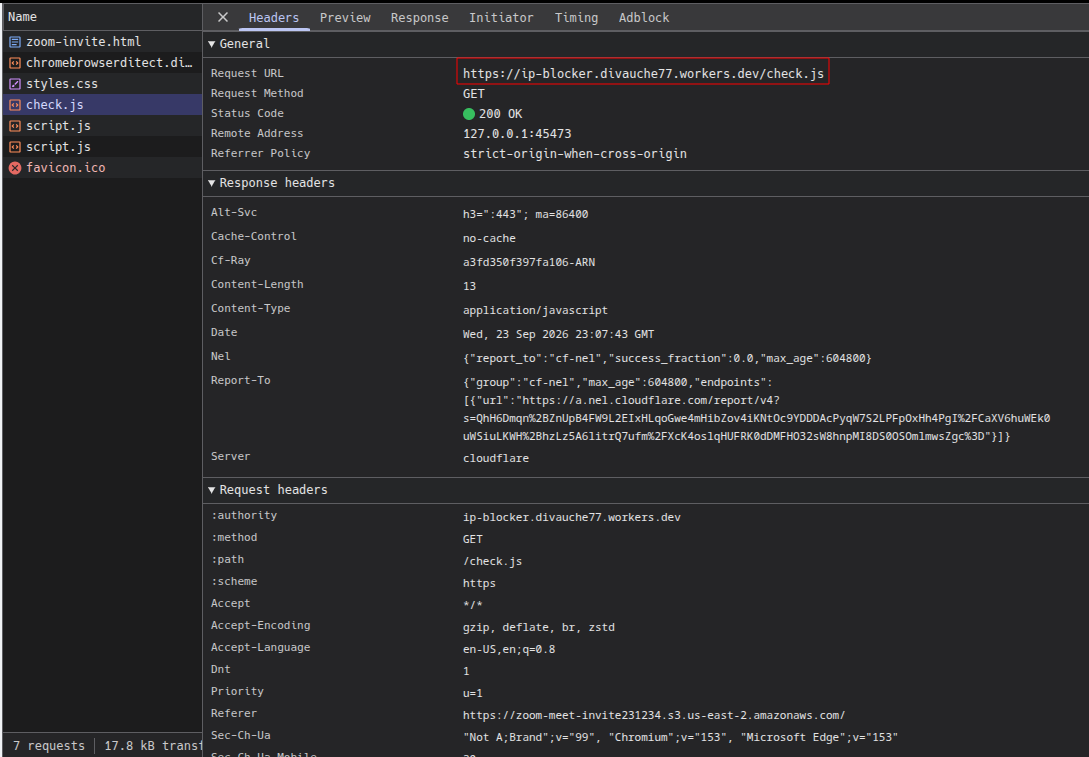

Opening the file in Malcat showed that the binary is Fleetdeck.
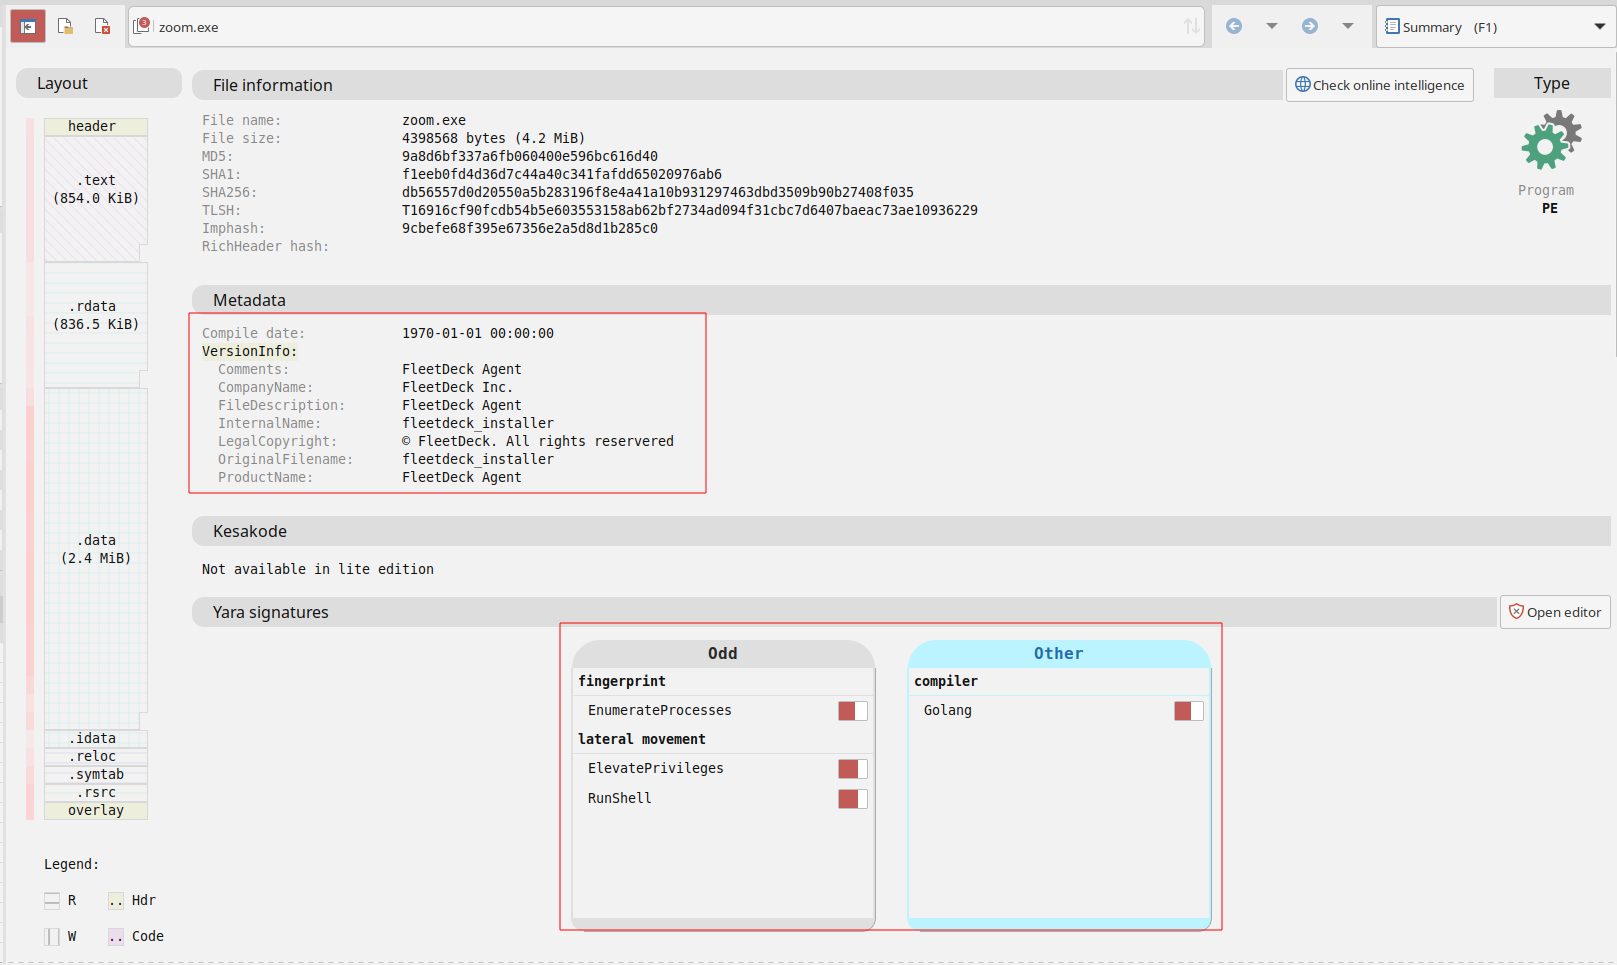

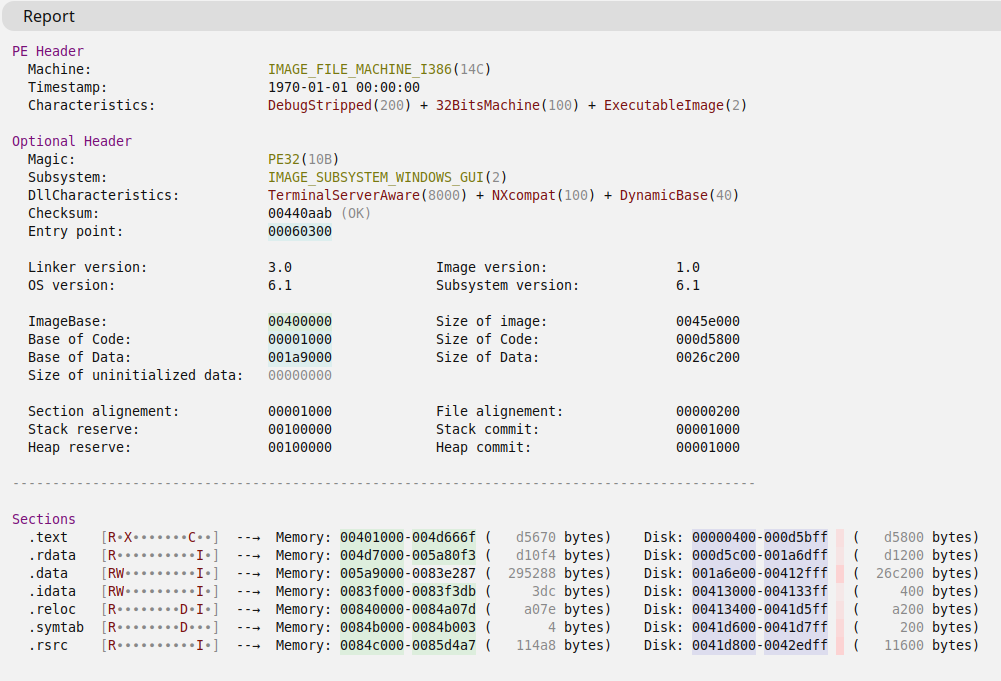

I didn't know what that was so, so I looked it up. Apparently, it is a RMM tool used to remotely manage computers. It was also written in Golang, so it was a pretty hefty binary. This was the PDB path found within the binary: "C:\agent\_work\66\s\build\ship\x86\wixca.pdb"
I am not great at reverse engineering, so I gave AI a go at the binary and see what it could find. It did a pretty good job at finding the embedded files, which were a fleetdeck_full.msi installer [0eb3b3136035ed9b30c1071cdbb69db06a871e04feda8a9cfe8e13ee82aa4d4b], a fleetdeck_agent_svc.exe [f7d793f458450f8da205887757af84967848fd42c8be78dfcd00524e6cf2ab65], a FleetDeckAgent_v1.0.0.cab file [361e8e988e372599f42875f59292727b45e66212dfb00dd774e72489c61c98a0], and a wixca.dll file [c8d190d5be1efd2d52f72a72ae9dfa3940ab3faceb626405959349654fe18b74].
VirustTotal Links for the files found as part of this analysis:
I also uploaded the samples to Hybrid Analysis as well:
IOCs
File hashes
| File | SHA256 | MD5 | Size |
|---|---|---|---|
| zoom.exe | db56557d0d20550a5b283196f8e4a41a10b931297463dbd3509b90b27408f035 | 9a8d6bf337a6fb060400e596bc616d40 | 4,398,568 |
| fleetdeck_full.msi | 0eb3b3136035ed9b30c1071cdbb69db06a871e04feda8a9cfe8e13ee82aa4d4b | 64de8b74901084b6c96a4a47fc97d564 | 2,449,408 |
| agent_svc.cab | 361e8e988e372599f42875f59292727b45e66212dfb00dd774e72489c61c98a0 | — | 2,110,912 |
| fleetdeck_agent_svc.exe | f7d793f458450f8da205887757af84967848fd42c8be78dfcd00524e6cf2ab65 | 2854313d8826aab27a90611b85ef3671 | 6,260,200 |
| wixca.dll | c8d190d5be1efd2d52f72a72ae9dfa3940ab3faceb626405959349654fe18b74 | a3ae5d86ecf38db9427359ea37a5f646 | 216,496 |
| embedded_wixca.dll | 2d6e754e9d045125ef146b215946ecfa4237e6193f3437a8cae46fa043a68a09 | ff6ecfd3721f337e188c9806ed5a94b3 | 208,384 |
| fleetdeck.ico | 83edd26056923ce34e062024808db7883fdd27bfee67163be03b90d80ce174bf | — | 68,433 |
Web Artifacts
| File | SHA256 |
|---|---|
| zoom-invite.html | da8dec7986a33522397f7057340350a3bdc9872e898eda2d24e11db93644767c |
| script.js | 8fad48b2acbae5e98cb914fc856085090bbf10755e9fba541875c2e97df71717 |
| script.js | 221cc5ac88c669baebe2b3d19f2952d27e92bd44a92cfe829da7185ba24af21a |
| check.js | a550c51e3174118bc155b02e33bd86a59df3aeed91ef26ac425b47f702166cf7 |
URLs
| Type | URL |
|---|---|
| Fake Zoom Url | zoom-meet-invite231234[.]s3[.]us-east-2[.]amazonaws[.]com/zoom-invite.html |
| Payload (live) | hxxps[:]//pub-1e9d6c57f6d543e99a4570a07bbe26ad[.]r2[.]dev/zoom[.]exe |
| Payload (fallback) | hxxps[:]//guj7fpdxwlardgjpvjsi7agm7i0rcpqb[.]lambda-url[.]eu-north-1[.]on[.]aws[.]com/ |
| Update endpoint | hxxps[:]//agentupdate[.]fleetdeck[.]io |
| Browser check | hxxps[:]//chromebrowserditect[.]divauche77[.]workers[.]dev/ |
| CSS | hxxps[:]//zooom-css[.]divauche77[.]workers[.]dev/styles[.]css |
| IP gate | hxxps[:]//ip-blocker[.]divauche77[.]workers[.]dev/check[.]js |
| Driver 1 | hxxps[:]//windows[.]divauche77[.]workers[.]dev/script[.]js |
| Driver 2 | hxxps[:]//zoom[.]divauche77[.]workers[.]dev/script[.]js |
| Beacon | hxxps[:]//downloadedreports[.]divauche77[.]workers[.]dev/ |
Messaging / other
| Type | Value |
|---|---|
| Telegram bot token | 8027979756:AAGwGffdv7YwzSFJabs8A2w9iQyqQgL6h3A |
| Telegram chat_id | 6955571616 |
| Fake meeting ID | meeting-1764987494729 |